
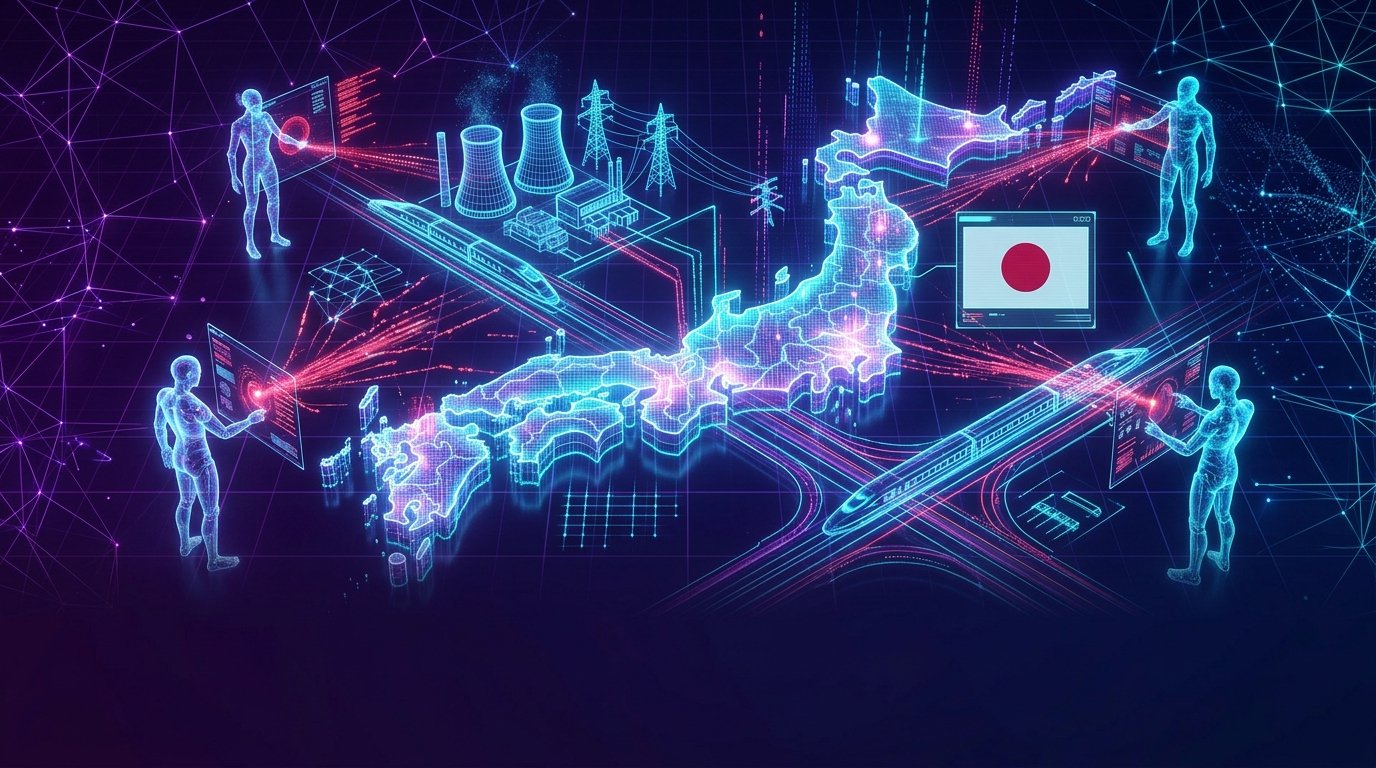
On Friday, October 23, 2026, the Japanese government announced the creation of a specialized national cyber unit tasked with using artificial intelligence to simulate sophisticated cyberattacks and hunt for vulnerabilities across critical technology systems, according to Shattered.io citing Reuters.
Why Governments Are Adopting Automated AI Red-Teaming
The announcement comes as global security teams scramble to patch over 1.5 million web servers exposed to the PHP2Shell vulnerabilities—flaws that were themselves uncovered with the assistance of advanced AI security auditing models.
Core Objectives of Japan's AI Red-Team Initiative
- Autonomous Exploit Simulation: Emulating how threat actors chain memory corruption and authentication bypasses in real time.
- Pre-Deployment Auditing: Scanning government and telecommunications software before public rollout.
- Closing the Speed Gap: Matching the machine-speed vulnerability discovery capabilities of state-sponsored adversaries.
When attackers use frontier AI to weaponize patches within hours, national defense requires continuous automated red-teaming.
Global Shift Toward AI-Assisted Vulnerability Discovery
Following the success of initiatives like Patch the Planet and DARPA's AI cyber challenges, national CERT agencies across Asia, Europe, and North America are embedding LLM-driven fuzzers into their standard defensive workflows.
Takeaways for Enterprise CISO Teams
Organizations should pair automated AI penetration testing with rapid container rebuild pipelines to shrink mean-time-to-remediate. Full primary documentation is available via Shattered.io Report on Japan's AI Cyber Simulation Unit.
Comments (0)
Leave a Comment