The Exploitation of Visual Trust Heuristics
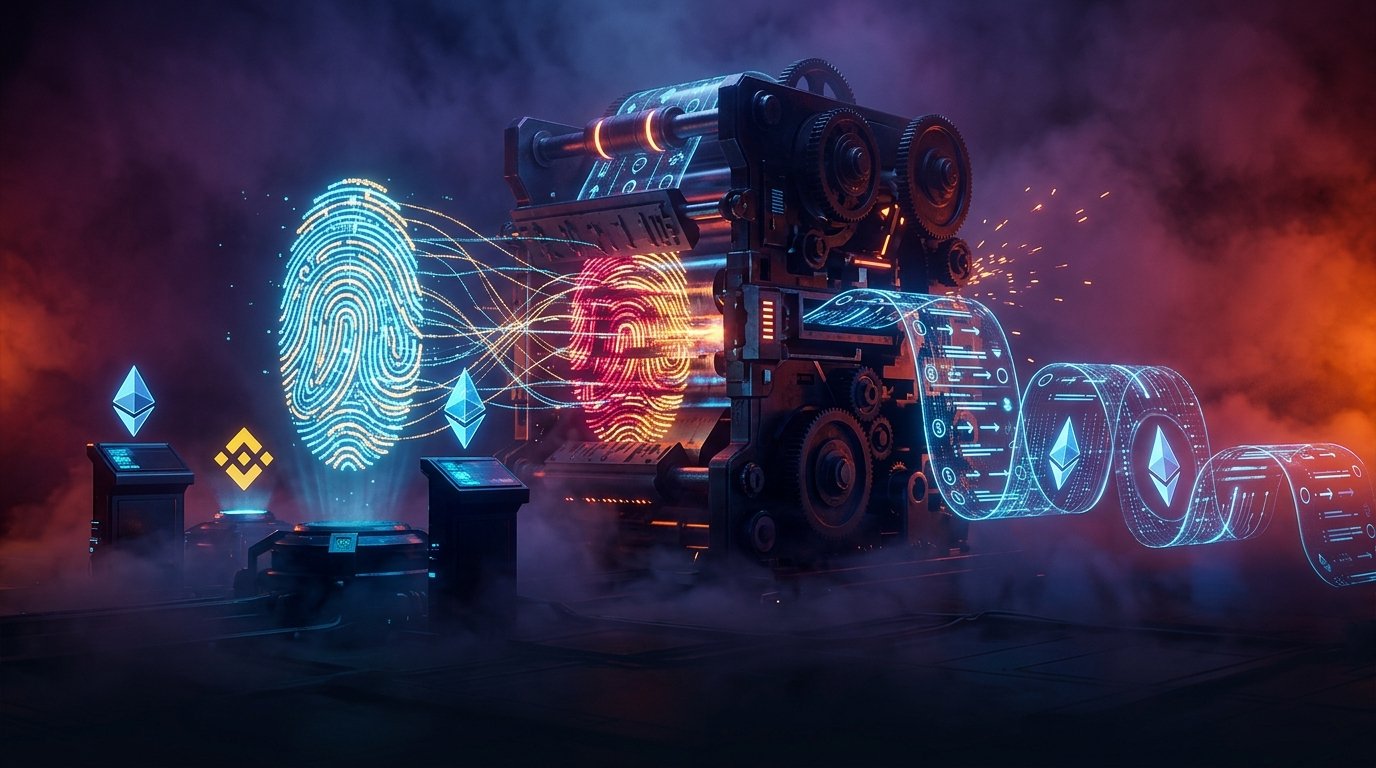
As blockchain security perimeters harden, attackers increasingly exploit human operational habits. Address poisoning has surfaced as a stealthy vector tricking Binance users into voluntarily directing outbound withdrawals to malicious destinations.
Algorithmic Generation of Look-Alike Addresses
The exploit exploits the human tendency to only visually verify the first and last few characters of complex hexadecimal strings:
You May Also Like
- Scammers monitor public mempools for high-volume transactions from active Binance deposit accounts.
- High-performance vanity address generators compute private keys yielding addresses matching the victim's prefix and suffix.
- The attacker initiates a zero-value transaction from the vanity address to the victim's wallet, injecting it into their history.
- When subsequent transactions occur, the victim mistakenly copies the spoofed address from their historical transaction log.
Because standard smart contract functions allow arbitrary addresses to emit transfer events, poisoning attacks require zero access to the victim's private credentials.
Defensive Configurations: Strict Whitelisting
Binance strongly advises users to disable transaction-history copy routines, maintain verified address books, and enforce the platform's mandatory Address Whitelist security feature.



Comments (0)
Leave a Comment